Workforce identity risk increasingly extends beyond recruitment and onboarding into password recovery, privilege changes and other moments when a compromised account can gain greater access. That creates a practical question for employers: when should an organization re-check the person behind a valid credential without turning security controls into continuous employee surveillance?
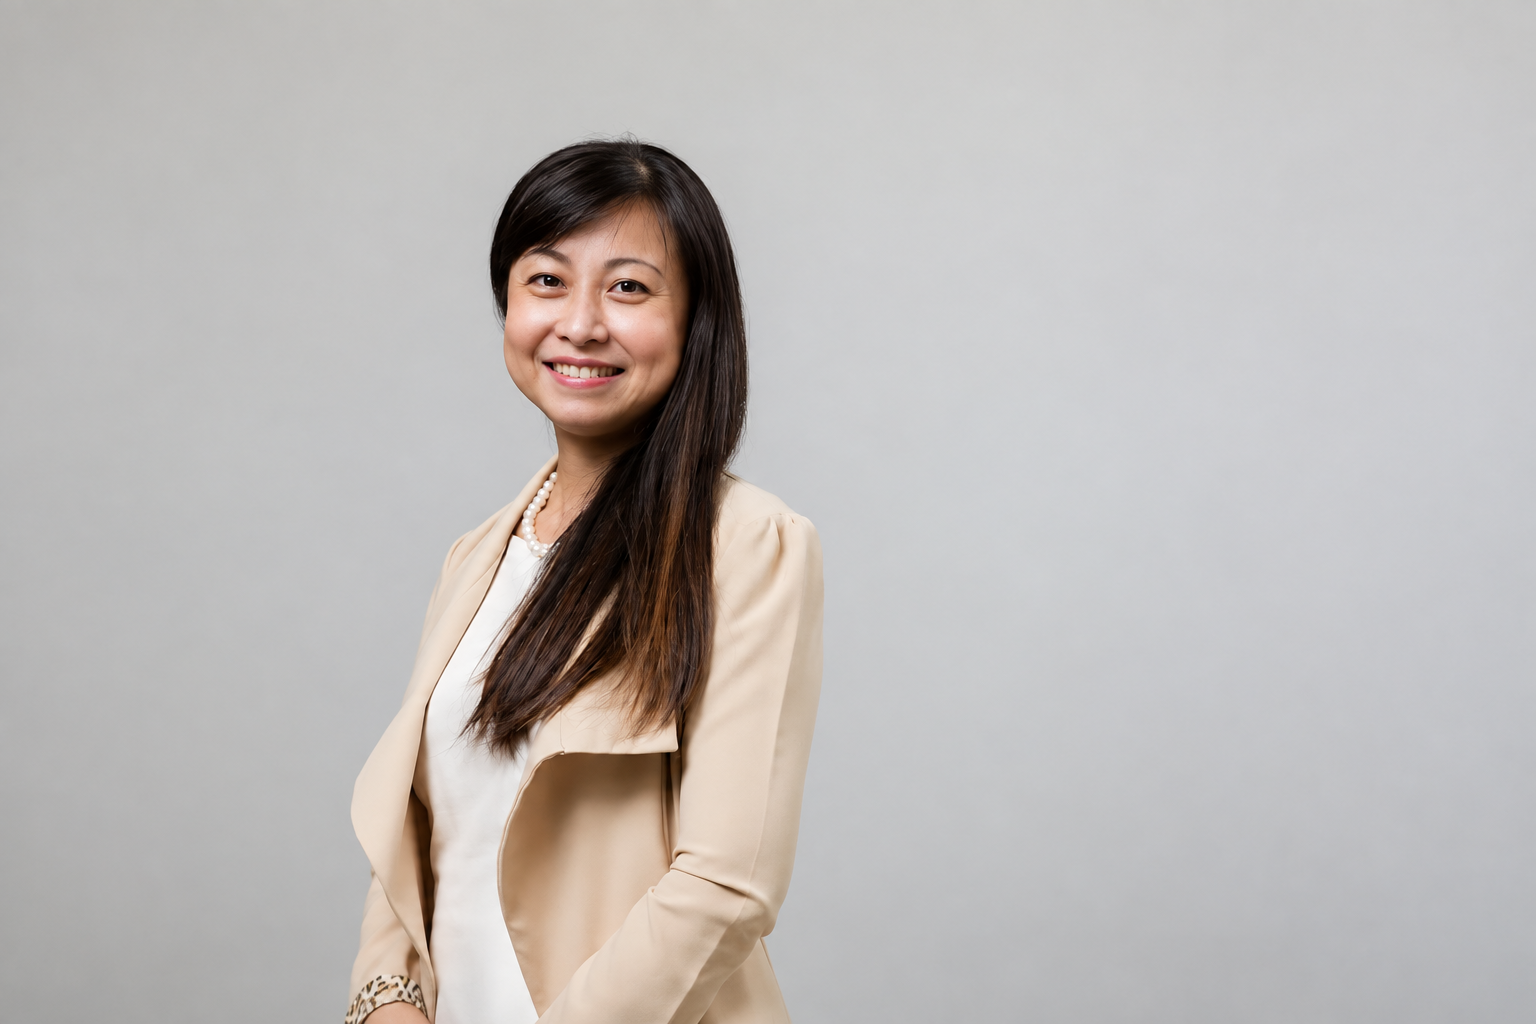
In this TNGlobal Q&A, Penny Chai, Vice President, APAC at Sumsub, discusses help-desk impersonation, event-driven identity checks, employee privacy, data retention and the separate governance problem created by AI agents and other non-human identities.
The discussion follows TNGlobal’s earlier coverage of Sumsub’s Workforce Verification launch. Product performance figures in the responses are company-supplied and should be read as such.
As remote hiring and distributed work become more common, where are organizations now seeing the most serious identity risks: recruitment, onboarding, account recovery, privilege changes, or another stage of the employee lifecycle?
Identity risk no longer sits at a single checkpoint but spans the entire employee lifecycle. The question is no longer just whether a new hire is genuine at onboarding, but whether the person taking a high-risk action later is still the authorized employee, not an attacker using stolen credentials, a deepfake or a socially engineered recovery request.
That being said, two moments stand out. The first is account recovery and the help desk, which Gartner flags as the leading driver of enterprise interest in workforce verification. Account recovery workflows often include knowledge-based questions, callbacks or colleague confirmation. These are sensible additional checks, but they can still depend on information an attacker has researched or socially engineered, or on a colleague’s ability to recognise a convincing impersonation. That makes account recovery a high-risk point in the employee lifecycle.
The second is the pre-hire and onboarding stage, where remote hiring has removed the old, implicit check of meeting someone in person. If a fraudulent identity clears that first gate, every credential and access right issued afterwards rests on a false foundation, which can lead to significant real world consequences. Someone wearing a trusted employee’s hat can reach sensitive assets and data a company cannot afford to lose. These include company finances, product source codes, or customer and investor records and the internal systems that keep the business running.
Credentials confirm that someone has an account, but not always that the authorized employee is using it at a high-risk moment. Workforce Verification closes that gap by establishing identity at onboarding and re-confirming it when consequential actions occur within existing IAM and HR workflows.
We saw this play out in 2025, when attackers impersonated an employee and talked a third-party help desk into resetting their credentials. That was enough to reach Marks & Spencer’s core systems, and the fallout cost the retailer roughly £300 million in operating profit. For any company, a single compromised identity in one market can give attackers the foothold they need to move laterally and infiltrate the wider network. For MNCs, the stakes are even higher. A breach today is rarely contained locally, but can quickly cascade across borders to put global operations at risk. That is why the priority shouldn’t be ranking the risk level of each of these stages against one another, but closing the identity gaps between them.
Help-desk impersonation and account recovery have become attractive attack paths because an attacker may already know enough personal information to sound convincing. What controls should organizations put around password resets and recovery workflows beyond adding another knowledge-based question or MFA step?
The core problem with knowledge-based questions is they assume the attacker doesn’t already have the answers. With AI-enabled social engineering, data leaks and information available across social platforms, that assumption is increasingly unsafe. In Singapore last year, we saw how effective these attacks can be when a Finance Director transferred S$670,000 after threat actors deployed real-time deepfakes on a Zoom call.
Raising the bar requires shifting from answers that can be researched or socially engineered to stronger evidence that the authorized employee is physically present. In practice, that means triggering a live identity check at the point of critical account recovery measures like password resets, combining deepfake-resistant biometric liveness checks to detect AI material, with passive background signals like device and location context. Sumsub’s proprietary Liveness technology can detect up to 99.98% of deepfakes in a single scan with real-time 3D mapping, adding an important layer of protection against AI-enabled impersonation. An organization cannot afford for its account recovery workflow to be its weakest link, especially when it is the primary target for modern threat actors.
Biometric liveness and document checks can help establish that a person is real and matches an identity document, but they do not prove that the person is trustworthy or that a request is legitimate. Where should organizations be careful not to overestimate what identity verification can solve?
Identity verification is a foundation, not the whole building. While it can confirm a person’s identity, it cannot predict intent or detect coercion. A properly verified employee can still act against the company, and a genuine user can still be coerced.
Where organizations often get into trouble is treating a positive identity check as a permanent green light. Identity verification must sit alongside least-privileged access guidelines and continuous behavioral monitoring to observe for suspicious or abnormal usage patterns when users are in the network. The true value lies in re-checking identity at critical, event-driven moments, while letting broader security controls govern what that verified person is actually permitted to do.
Workforce verification can also raise concerns about employee privacy and surveillance. How should employers decide when a step-up identity check is proportionate, what data should be retained, and how often should a worker be asked to re-verify?
Proportionality has to be the baseline. Otherwise, you end up surveilling employees under the guise of protecting them, which few will accept. The principle we work towards is that verification should be event-driven rather than a constant, so most of an employee’s day involves no visible check at all. Passive controls can assess context quietly in the background, while an active step-up, like a biometric liveness check, is triggered only when there is a meaningful change in risk: for example, an attempt to reset a password, enrol a new device, access a sensitive system, approve a payment or move into a higher privilege role.
In practice, that means organizations need configurable workflows. They should be able to define which events require a step-up, which contextual signals can remain passive, and what level of evidence is proportionate for each use case. Forcing re-verification on a fixed timeline treats everyone as a suspect and will encourage the workarounds companies were trying to prevent in the first place.
On data retention, the discipline is minimization. Collect only what a specific check requires, and be transparent with employees about what is captured, why it is needed, and how it will be used. Biometric material, in particular, demands clear governance, tight access controls and defensible retention practices. Frequency should follow risk in the same way. Re-verifying because a high-risk circumstance has changed is easier to justify; re-verifying because a calendar quarter has passed is much harder to defend.
Which events should realistically trigger renewed identity verification after onboarding, such as password resets, device changes, privilege escalation, unusual locations or access to sensitive systems? How can companies avoid creating so much friction that employees begin looking for workarounds?
The realistic triggers are the moments where the cost of a compromised identity drastically escalates. These include account recovery or password resets, enrolment of a new device or authenticator, step-ups into privileged access, and attempts to reach sensitive systems or to log in from an unusual location.
Managing friction is the critical half of this equation. If verification prompts fire constantly, employees will end up actively routing around it, and a control that people evade is worse than no control at all because it provides a false sense of security.
The answer is a risk-based system rather than blanket enforcement. Passive signals, such as device and location context, can operate across routine activity with little or no employee interruption. Active checks should surface only when the risk profile changes materially or when the requested action has significant consequences.
Done well, most employees will rarely see a prompt, and when they do, the reason is clear enough that it feels reasonable rather than punitive. Embedding those checks into existing IAM and HR workflows also matters, because a familiar and clearly explained process is less disruptive than a separate, disconnected security hurdle.
Multinational employers operate across very different privacy, biometric and employment-law regimes. What are the biggest challenges in deploying a consistent workforce-verification policy across Asia Pacific without simply applying the most intrusive control everywhere?
Navigating Asia-Pacific is complex because the region is not a single regulatory regime, but a patchwork of many. What an organization is allowed to collect, along with regulations on consent and data localisation, varies sharply from one market to the next. A common mistake is attempting to resolve this by imposing the strictest control across the region, which needlessly introduces friction into markets that never needed it and increases the amount of sensitive data an organization is collecting without a clear proportionality case.
What works best is maintaining consistency at the level of risk and outcome. The standard for what triggers a check should remain the same across regional (or global) operations for example, requiring stronger identity assurance before a password reset for a privileged account or before access to a highly sensitive system. But the underlying legal, consent, data-handling and verification configurations should be localized to fit the market.
The objective is the same: verify the person behind a high-risk action. The route to achieving that objective may need to differ depending on what local law permits, what employees reasonably expect and how the organization’s local systems are configured. This is why a configurable workforce verification layer is important. It allows employers to apply a common global risk framework while adapting workflows, data handling and retention to local requirements.
Sumsub describes Workforce Verification as a layer over existing IAM and HR systems. What information should remain with the identity-verification provider, what should stay with the employer, and how should organizations avoid creating another central repository of highly sensitive employee data?
An identity verification layer should complement an enterprise’s existing infrastructure, not replace it. Crucially, it should avoid becoming another central repository of sensitive employee data. The guiding principle is to leave core responsibilities where they belong. IAM platforms continue to enforce access policies and decisions, while HR maintains employee records. Security teams should continue to own the wider security policy, incident response and access-governance framework.
What the verification layer adds is real-time identity assurance at high-risk moments, confirmation that it was a genuine, matching identity, and passing that decision back into existing systems rather than building a permanent archive. The discipline that makes this safe is minimization, which means capturing only what a specific check needs and holding it only as long as the purpose requires.
As a rule of thumb, organizations should expect any verification provider, including Sumsub, to support clear data retention settings, deletion processes, robust access safeguards and auditable controls, in line with the employer’s privacy policies and applicable legal requirements.
What metrics tell an organization that workforce verification is actually reducing risk? Beyond the number of checks completed, what should security and HR teams watch around attempted impersonation, false positives, recovery fraud, employee friction and bypass behavior?
Volume of checks is an activity metric, not a risk metric, and should never be used as a key indicator. Meaningful metrics must be evaluated in balanced pairs.
On the security side, teams should track step-up interception rates alongside the reduction in successful account-recovery fraud, which we’ve established is often the primary target for these attacks. On the employee experience side, the false-positive challenge rate must trend downward, as unnecessary friction quietly erodes internal trust.
Operational efficiency matters just as much, where manual review volumes and handling times show whether the process can scale. Sumsub has observed well-executed deployments being able to reduce manual verification workloads by up to 94%. Finally, bypass behavior should be closely monitored, as any uptick in workarounds is the earliest signal that controls are poorly calibrated.
As AI agents and non-human identities begin operating alongside employees, how should organizations separate human identity proofing from the governance of service accounts, bots and AI agents that may ultimately receive similar access to internal systems?
Human identity proofing and non-human identity governance address fundamentally different security challenges, and the primary risk lies in treating them as identical.
Human verification relies on inherent biometrics, liveness, and official credentials to confirm a real employee is present. AI agents, bots and service accounts have none of these attributes, rendering human proofing methods entirely irrelevant. What enables effective management of non-human identities is instead rigorous governance. This means a designated, accountable human owner for every agent, along with tightly scoped, short-lived credentials that are deliberately retired after each use case, as well as a clear audit trail of what it is authorized to do.
That need is becoming more urgent as AI systems take on more autonomous work. Sumsub’s recent AI Governance Benchmark found that 94% of Singapore businesses are already using or piloting multi-step AI systems with limited human input, yet only 29% can produce an audit trail explaining an AI-driven decision. The challenge is no longer simply adopting AI; it is maintaining clear accountability as AI acts across business systems.
Regardless of how autonomous an AI agent becomes, its access must trace back to a verified human who remains answerable for its actions. Whether human or machine, all network access must map back to an identity that a verified human with the right authority has vouched for.
That is why Sumsub introduced AI Agent Verification under its Know Your Agent (KYA) framework. It binds an AI agent’s activity to a real, verified human identity, helping organizations distinguish authorized automation from malicious activity and establish a clear line of accountability without treating all automation as inherently suspicious.
Penny Chai is Vice President of APAC at Sumsub. She joined the company in April 2023 and has more than 25 years of international experience in partnerships, business development and marketing. Her previous roles include Director of Global Partnerships at Merkle Science and Channels Director, APAC at Jumio, as well as senior positions at Zebra Technologies, Intermec Technologies, Dell Global BV and Hewlett-Packard. She is based in Singapore.
Editor’s note: This Q&A has been edited for clarity and TNGlobal house style. The substance of the interviewee’s responses, including views and attributed claims, has been preserved.
Share your perspective: TNGlobal welcomes contributed insights and expert commentary from across Asia’s technology and innovation ecosystem. Submit a contribution for editorial consideration, or explore more conversations in our TNGlobal INSIDER and TNGlobal Q&A and Interviews archive.
Sumsub adds biometric workforce verification to account recovery and access workflows