As AI agents move beyond answering questions and begin acting on behalf of employees and customers, identity controls become a question of who has the authority to do what, and when that authority should expire. The same system that can speed up routine work can also create difficult questions around access rights, accountability and consent.
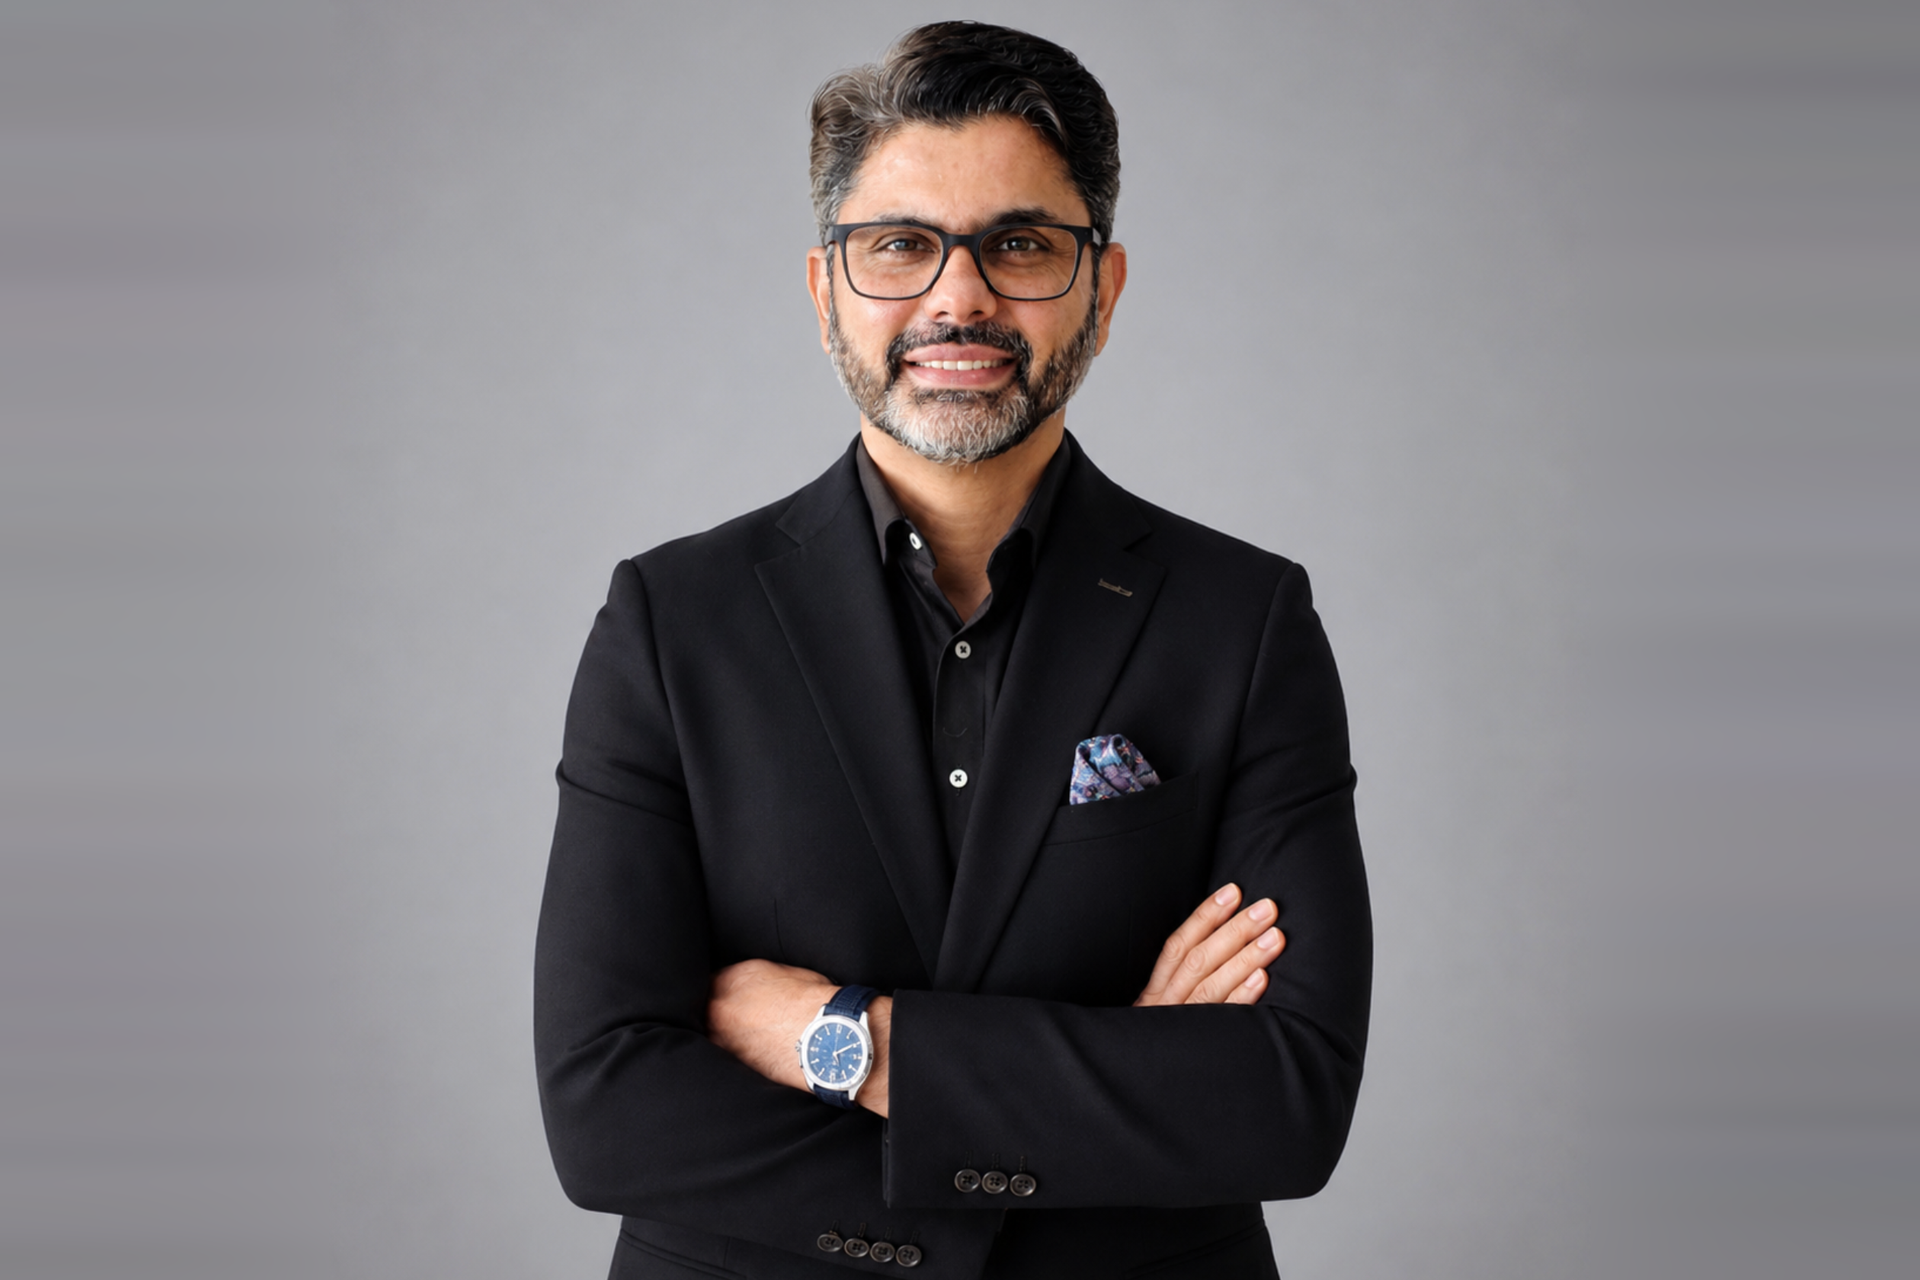
In this TNGlobal Q&A with Akkasha Sultan, Senior Vice President and General Manager for Asia Pacific and Japan at Ping Identity, we discuss how businesses can assign identities to AI agents, limit delegated authority, preserve audit trails and keep humans involved in consequential decisions. Sultan also examines what consumer trust in agentic AI should mean beyond adoption figures.
The conversation follows Ping Identity’s research on Singapore consumers’ attitudes toward AI autonomy and the guardrails they expect as these systems take on more responsibility.
As AI agents move from making recommendations to taking actions on a user’s or company’s behalf, how should organizations decide the limits of delegated authority? Which permissions should an agent never receive by default?
The starting point is to align an agent’s authority with the business outcome it is expected to deliver. Organizations should assess the potential impact of each action, the sensitivity of the information involved and the consequences of an error. An agent tasked with researching suppliers, for example, should not automatically have the authority to sign contracts or release payments.
This requires organizations to establish clear boundaries around what agents can decide independently, what they can execute within predefined limits and what requires escalation. Those boundaries should reflect business risk, regulatory obligations and the expectations of the people represented.
Importantly, delegation should never be interpreted as unrestricted authority. Agents should not receive blanket administrative privileges, unrestricted access to sensitive records or permission to override established controls.
The goal is to enable autonomy with purpose: giving AI room to deliver value without allowing its authority to exceed its mandate.
What does it mean in practice to bind an AI agent to the identity of the person or business it represents? How can organizations prevent an agent from continuing to act when the underlying user’s role, account status or authorization has changed?
An AI agent needs a distinct identity of its own, alongside a verifiable relationship with the person or organization it represents. This allows systems to distinguish between the agent performing an action and the human or business whose authority underpins it. Simply allowing an agent to operate using a person’s credentials obscures that distinction and weakens accountability.
In practice, organizations need to establish who created or authorized the agent, the capacity in which it acts and the scope of its delegation. That relationship must also reflect changes in employment, account status and business responsibilities.
For example, when an employee leaves an organization, their agent should not retain the ability to access corporate systems simply because previously issued credentials remain valid. Changes to the underlying identity must trigger corresponding changes to the agent’s authority.
Identity establishes representation; authorization determines what that representation permits.
How should permissions for AI agents be issued, narrowed and revoked over time? Are short-lived credentials and least-privilege access sufficient, or do agentic systems require additional controls?
Agent permissions should be managed as a lifecycle, rather than a one-time provisioning exercise. At creation, organizations should define the agent’s purpose, owner, permitted resources and duration of access. As its task progresses, permissions should be restricted to the specific operations required, avoiding broad or persistent access that creates unnecessary exposure.
Short-lived credentials help reduce the window in which compromised access can be exploited, while least-privilege policies limit the potential damage. However, both need to be supported by controls that detect changes in risk, unusual behaviour and attempts to exceed the original mandate.
Organizations should also establish clear expiry conditions, periodic reviews and automated revocation mechanisms. An agent whose purpose has ended, whose sponsor has lost authority or whose behaviour raises concerns should no longer be able to act.
The emphasis should be on managing access dynamically, ensuring permissions evolve with the task rather than accumulating over time.
If an AI agent takes an action across several services, what should a useful audit trail contain so that an organization can reconstruct who authorized the action, what the agent accessed and why the action was allowed?
An effective audit trail should provide a reliable reconstruction of an agent’s activity across the entire transaction or workflow. Investigators need to establish the sequence of events, the systems involved, the information accessed and the resulting changes—not merely confirm that individual API calls occurred.
Records should capture the agent’s unique identifier, the initiating request, timestamps, affected resources, actions performed, authorization decisions and outcomes. Where an action relies on a human approval or a specific policy exception, the audit trail should preserve that context. Consistent identifiers across services are particularly important for correlating activity across otherwise disconnected systems.
Organizations should also protect logs against tampering and restrict access to sensitive audit information. Retention policies must support investigation and regulatory requirements without unnecessarily exposing personal data. A strong audit trail turns AI activity into evidence that can be independently examined, helping organizations investigate incidents, demonstrate compliance and establish responsibility.
Where should human approval remain mandatory? Are there particular actions involving money, identity data, account recovery or changes to access rights where autonomous execution should remain off-limits?
Human approval should be reserved for decisions where the potential consequences justify an additional layer of judgment and accountability. This includes significant financial transfers, sensitive account recovery, changes to privileged access, high-impact identity changes and decisions that could materially affect a person’s rights or access to essential services.
The distinction is not whether AI can technically perform these actions, but whether it should be empowered to do so independently. An agent may prepare a payment, verify supporting information or recommend an access change without receiving final authority to execute it.
Organizations should define approval thresholds according to risk, transaction value, sensitivity and reversibility. They should also consider whether the approver has sufficient context to make an informed decision, rather than treating approval as a routine click-through.
Over time, lower-risk activities may be automated as controls mature and evidence supports doing so. Human oversight is most effective when it is targeted at consequential decisions, rather than imposed indiscriminately across every interaction.
Consumers may authorize an agent in one service and then expect it to act across other platforms. What technical and governance problems emerge when delegated identity and permissions have to travel across organizational boundaries?
Cross-organizational delegation introduces a fundamental challenge: one organization’s confidence in an agent does not automatically establish trust for another. A consumer might authorize an agent to purchase a product, but the retailer, payment provider and delivery service each have their own security requirements, policies and responsibilities.
Organizations must determine whether the agent’s identity can be verified, whether the original delegation is authentic and whether the requested action falls within its scope. Differences in identity standards, consent mechanisms and authorization models can make these checks inconsistent. Revoking permission is equally challenging if the change does not propagate to every participating service.
Governance must address liability, data-sharing responsibilities and how disputes are resolved when an agent acts across multiple organizations.
Interoperable standards can help establish a common basis for verifying identity and delegated authority, but technical integration alone is insufficient. Scalable agentic ecosystems will depend on shared trust frameworks that allow organizations to cooperate without surrendering control over their own security policies.
Ping’s Singapore findings suggest people are open to giving AI more responsibility but remain concerned about representation, oversight and data use. What would you look for to distinguish genuine trust in an AI agent from adoption driven mainly by convenience?
Convenience can accelerate adoption, but it does not necessarily demonstrate confidence. People may use AI because it saves time while remaining uncertain about whether it represents their interests, handles their information appropriately or makes decisions they would endorse.
Ping Identity’s consumer research points to this tension. Its Singapore findings indicate that people can be receptive to AI taking on greater responsibility while remaining concerned about misrepresentation and the handling of personal information. This makes transparency and user control important indicators of trust.
Organizations should look beyond usage rates to understand whether consumers know what they have authorized, can explain how an agent acts on their behalf and feel comfortable changing or withdrawing permissions. They should also assess confidence following mistakes or unexpected outcomes, when trust is genuinely tested.
Genuine trust exists when people understand the relationship, believe their interests are protected and remain willing to delegate—not simply when using AI is the easiest option.
For organizations deploying agentic AI now, which metrics or failure signals would tell you that the identity and authorization layer is working as intended rather than simply adding another login or security control?
Organizations should assess whether identity and authorization controls improve both security outcomes and operational performance. A useful starting point is visibility: how many deployed agents have identifiable owners, documented purposes and approved access scopes? Without that baseline, organizations cannot reliably establish whether their agent population is under control.
They should then measure the effectiveness of enforcement, including unauthorized requests blocked, anomalous activities detected, excessive privileges identified and access revoked when required. Incident response metrics can reveal whether teams can investigate agent behaviour quickly and establish the source of a decision.
Business performance matters too. Monitor legitimate task-completion rates, delays caused by unnecessary approvals and recurring authorization failures. A system that blocks everything may be secure in a narrow sense but is unlikely to support adoption.
The strongest signal is a measurable reduction in identity-related risk without creating disproportionate friction for legitimate AI-driven work.
Akkasha Sultan is Senior Vice President and General Manager for Asia Pacific and Japan (APJ) at Ping Identity. He has more than 25 years of experience in technology leadership, including roles at Salesforce and Tableau spanning enterprise AI, analytics and regional business operations.
Editor’s note: This Q&A has been lightly edited for clarity and TNGlobal house style. The substance of the interviewee’s responses has been preserved.
Share your perspective: TNGlobal welcomes contributed insights and expert commentary from across Asia’s technology and innovation ecosystem. Submit a contribution for editorial consideration, or explore more conversations in our TNGlobal INSIDER and TNGlobal Q&A and Interviews archive.
Ciena’s Gautam Billa on connecting distributed AI data centers across Asia