Singapore security teams reported relatively strong awareness of AI-generated phishing in a 2026 survey by Yubico and Okta, but awareness has not eliminated the threat. Among surveyed IT and cybersecurity professionals in Singapore, 58 percent said their organizations had experienced at least one successful AI-driven phishing attack during the previous year, while 81 percent reported enforcing multifactor authentication across applications and services. These are self-reported findings rather than independently verified incident counts.
The findings raise questions about the authentication methods companies rely on, including one-time codes and push notifications, and where more phishing-resistant credentials can reduce exposure. They also point to a newer identity challenge as autonomous AI agents begin accessing enterprise applications and taking actions on behalf of people.
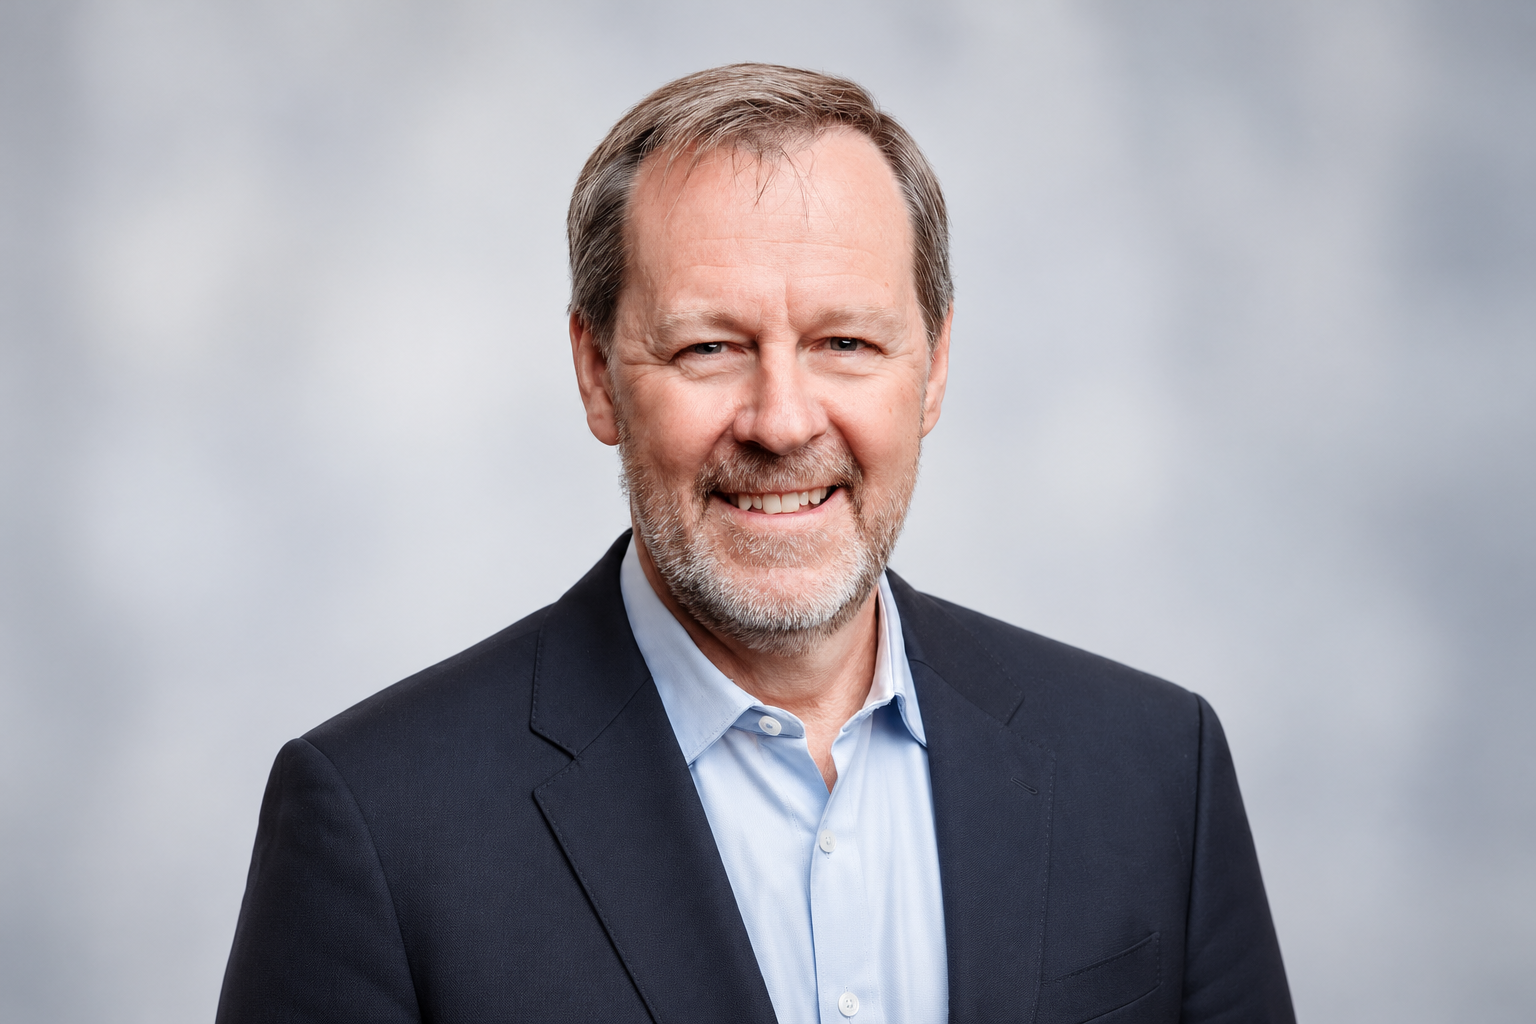
In this TNGlobal Q&A with Geoff Schomburgk, Regional Vice President for Asia Pacific and Japan at Yubico, we discuss the survey findings, the limits of conventional MFA, practical migration paths toward phishing-resistant authentication and the safeguards needed when AI agents act with delegated authority.
Singapore respondents were comparatively good at identifying AI-generated phishing, yet 58 percent still reported at least one successful AI-driven phishing attack in their organization. How should security teams interpret that gap between awareness and actual compromise?
The findings highlight the limitations of relying on employees to identify every phishing attempt, especially in the face of AI-driven threats.
While Singapore respondents were the most successful among surveyed markets at spotting AI-generated messages, this does not necessarily translate into protection against actual attacks.
Organizations need to shift their focus from expecting employees to recognize every threat, to implementing controls that prevent credential compromise.
Traditional MFA methods, including SMS codes, one-time passwords and certain push-based methods, remain vulnerable to phishing. Phishing-resistant authentication, such as FIDO2 hardware security keys, uses cryptographic authentication bound to the legitimate service, preventing attackers from using fraudulent login pages to capture reusable authentication credentials.
The priority is to reduce dependence on human judgment at the point of authentication, rather than treating awareness training as the primary safeguard.
What did the survey classify as a successful AI-driven phishing attack, and how confident can organizations generally be that AI was materially involved in an attack rather than simply suspected after the fact?
The respondents surveyed, all IT and security professionals, were asked if their organization had experienced at least one successful AI-driven phishing attack during the past year. Over half indicated that this was so for their companies.
In practice, determining whether AI was materially involved in an attack can be challenging. Security teams may examine evidence and other operational signatures like speed, large scale hyper-targeted variations, automated multi-channel follow-ups, and synthetic voice or video impersonations.
Regardless of whether a phishing attempt was created by a person or generated using AI, organizations must protect against credential theft and unauthorized account access. Establishing AI’s role is useful for understanding evolving attacker techniques, but it should not distract from addressing the underlying security weaknesses.
Eighty-one percent of respondents say MFA is enforced across all applications and services, but passwords, TOTP and push authenticators remain common. Which attack paths remain open when organizations have MFA but not phishing-resistant authentication?
MFA provides an important layer of protection, but not all methods are equally resistant to phishing. Adversary-in-the-Middle (AiTM) phishing, for example, uses reverse-proxy sites that intercept usernames, passwords, and even real-time TOTP codes or push responses to hijack accounts instantaneously.
SMS-based authentication is also exposed to risks such as SIM swapping, while push-based methods can be exploited through MFA fatigue attacks, where users receive repeated fraudulent approval requests until they inadvertently approve one.
Phishing-resistant authentication addresses these weaknesses by using cryptographic credentials bound to the legitimate service. With FIDO2 hardware passkeys, authentication cannot be completed through an impersonating website, even if an employee is deceived into visiting it.
However, organizations must also secure active sessions, endpoints and account recovery processes. Stronger authentication significantly reduces credential-phishing risks, but it remains one component of a broader identity security strategy.
Only 26 percent reported using hardware security keys for work accounts. What are the biggest barriers to broader adoption in Singapore, and where should organizations prioritize phishing-resistant authentication first if they cannot migrate everyone at once?
One key challenge we’ve seen is that organizations often introduce stronger authentication methods without fully replacing older ones. In Singapore, 72 percent of respondents say their organizations use different authentication methods across applications. This suggests that businesses may be managing increasingly complex authentication environments, rather than consistently moving away from weaker methods.
If an organization cannot migrate everyone at once to hardware passkeys, deployment should follow a risk-tiered approach. The initial focus should be on securing high-impact accounts such as IT or cloud administrators, C-suite executives, finance managers, and employees with access to sensitive information or critical systems.
The longer-term objective should be to simplify authentication across the workforce, integrating stronger methods into existing workflows while retiring weaker options wherever possible. Security improvements are more likely to be sustained when they reduce friction for employees rather than adding another layer of complexity.
As AI agents begin accessing enterprise systems, how should identity teams authenticate the agent itself, the human or service that authorized it, and the specific permissions it is allowed to exercise?
Organizations need to establish who or what is acting, whose authority they are acting under, and what they are permitted to do.
Identity platforms can authenticate AI agents and enforce access policies, but this does not necessarily prove that a specific human authorized an agent’s actions. Organizations need to address both identity and human authorization, particularly as AI agents gain more access to sensitive systems and carry out consequential tasks
For actions requiring human authorization, hardware-backed verification can provide cryptographic proof that an authorized individual approved a specific action. This creates a stronger link between the agent’s activity and the human responsible for authorizing it.
Organizations also need access policies and runtime authorization controls to determine which actions an agent is permitted to perform. These controls complement hardware-backed human authorization, helping ensure that an agent operates within its approved scope.
The key is to connect agent identity, access controls and verified human authorization, so organizations can establish not only which agent performed an action, but whether that action was appropriately authorized.
Ninety-five percent of respondents say actions should be reviewed before an AI agent executes them. How can organizations preserve meaningful human approval without creating another form of approval fatigue?
Human oversight remains important as AI agents take on greater responsibilities, but requiring approval for every routine task could quickly become impractical.
A human-in-the-loop approach allows AI to act autonomously in most cases, but requires cryptographically verified human approval when the stakes are high. Routine administrative tasks may require minimal oversight, while actions involving financial transactions, sensitive information or changes to critical systems should warrant closer scrutiny.
Importantly, employees need sufficient context to make informed decisions. An approval request should clearly explain what the agent intends to do, which systems or information are involved, and the potential consequences, rather than simply presenting another notification to acknowledge.
For higher-risk actions, that oversight should be backed by strong authentication, such as a security key touch or biometric verification, to help establish that the person approving the action is who they claim to be.
The objective is not to introduce more approval steps, but to ensure meaningful human intervention at critical decision points.
Fifty-eight percent of respondents were initially issued usernames and passwords when joining their organization. What would a realistic migration path look like for companies that want to move away from password-first onboarding without disrupting existing systems?
Where possible, organizations should integrate stronger authentication into employee onboarding from their first day. When usernames and passwords remain the default during onboarding, businesses risk reinforcing the same practices they are trying to replace.
A realistic migration can take place in phases. Before authentication, organizations can work toward issuing phishing-resistant credentials during employee onboarding and verifying device health. During authentication, they can enforce phishing-resistant methods through application sign-on policies. Beyond implementation of authentication, continuous context and risk evaluation can help detect potential session compromise.
For new employees, hardware-backed credentials should be issued during onboarding, enabling secure access from their first login rather than introducing stronger authentication as an additional requirement later.
Existing employees can be migrated progressively, supported by clear instructions, recovery procedures and consistent access policies. For legacy applications that still require passwords, centralized identity management and single sign-on can help reduce the number of separate credentials employees must manage.
The goal is to replace insecure defaults, rather than simply adding another authentication method alongside them. This requires organizations to consider the entire employee experience, from onboarding and daily access to account recovery.
Over the next 12 to 24 months, which measures would show that an organization has actually reduced identity risk rather than simply deployed more authentication tools?
Progress should be determined by whether organizations have reduced opportunities for attackers to compromise identities, rather than the number of authentication tools deployed.
A starting point is the proportion of employees and applications protected by phishing-resistant authentication, particularly privileged accounts and critical systems. Organizations should also track whether reliance on passwords and other vulnerable methods is declining.
Onboarding provides another useful measure. If new employees continue receiving passwords as their default credentials, organizations are perpetuating the same risks despite investing in stronger authentication.
Security teams should also monitor credential-related incidents, account compromises and attempts to exploit weaker authentication or recovery processes. Beyond the initial login, they need visibility into endpoint security and active sessions, where stolen session tokens or compromised devices can introduce further risks.
As AI agents become more prevalent, organizations should also assess whether agents have identifiable credentials, appropriately restricted permissions and auditable activity, with human approval for higher-risk actions.
Ultimately, the measure of progress is whether attackers have fewer opportunities to compromise accounts, exploit excessive permissions or move through an organization’s systems using stolen identities.
Geoff Schomburgk is Regional Vice President, Asia Pacific and Japan, at Yubico. He works with enterprise customers and partners on phishing-resistant authentication across the region. He has more than 30 years of experience in the information and communications technology industry, including executive, engineering and strategy consulting roles.
Editor’s note: This Q&A has been lightly edited for clarity and TNGlobal house style. The substance of the interviewee’s responses has been preserved.
Share your perspective: TNGlobal welcomes contributed insights and expert commentary from across Asia’s technology and innovation ecosystem. Submit a contribution for editorial consideration, or explore more conversations in our TNGlobal INSIDER and TNGlobal Q&A and Interviews archive.
https://technode.global/2026/10/29/ping-identity-akkasha-sultan-ai-agent-identity-trust-qa/