Digital sovereignty is increasingly shaping decisions about cloud, artificial intelligence, networking and data architecture across Asia Pacific, where multinational companies must operate across markets with different regulatory and infrastructure conditions.
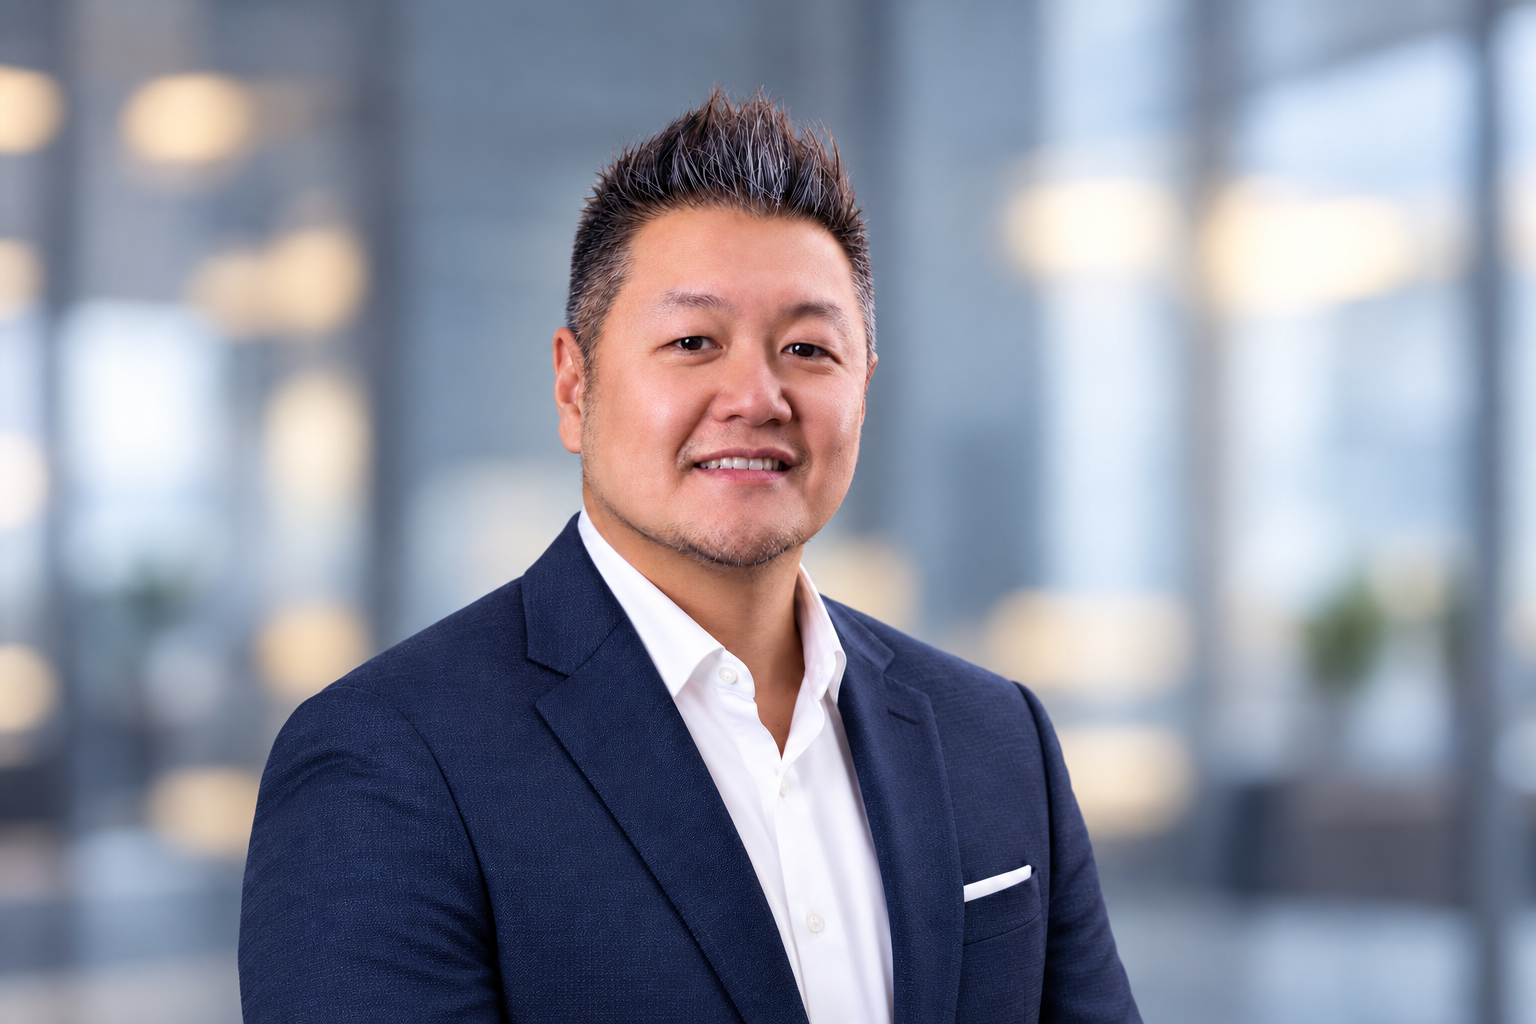
In this TNGlobal Q&A, Eric Wong, President of Asia Pacific and Global Wholesale at Expereo, discusses sovereignty beyond data residency, hybrid network architecture, AI dependencies, workload classification, localization trade-offs and what boards should ask to determine whether sovereignty controls work in practice.
When a multinational company says it wants greater digital sovereignty, what should that mean in practical architecture and governance terms beyond simply keeping data in a particular country?
At its core, digital sovereignty is about maintaining meaningful control over data, workloads and the infrastructure connecting them. It should not be reduced to keeping data within national borders. Business leaders need a clear view of what data their organization holds, where it moves, who can access it, and which providers and jurisdictions are involved. From there, they can decide which workloads must remain local, which can operate regionally and which can safely use global services.
In practice, this points toward a hybrid sovereign network: secure, low-latency access to local infrastructure where national obligations demand it, connected to regional and global services through a consistent, compliant fabric. The goal is not to localize everything, which can add cost and complexity, but to maintain the visibility, governance and operational control needed to meet local requirements without fragmenting the wider business.
APAC companies operate across very different data-residency, privacy and cybersecurity regimes. Where do you see the biggest operational friction when a company tries to apply one cloud and AI architecture across several markets?
The biggest challenge is assuming that APAC can be treated as one uniform operating environment. A common cloud and AI architecture may look efficient from a central perspective, but if you look closely the reality on the ground is far more complex.
Regulatory expectations, cloud access, infrastructure maturity and the behavior of cross-border traffic vary considerably across markets. I’ve always said that businesses expanding in APAC need to make region-specific decisions rather than rely solely on globally consistent templates. For example, our latest survey findings show that Thailand stands out on cross-border data transfer concerns, Indonesia on alignment with national digital sovereignty policies, and Vietnam on geopolitical risk. Multinational businesses therefore need a consistent regional framework for governance, with enough flexibility to respond to local conditions. Without that balance, they risk imposing a model that does not work locally or creating disconnected environments that are costly and difficult to manage.
Expereo argues that the network is becoming part of the sovereignty discussion. What network-level controls or visibility actually help a company understand where data and traffic are moving, and where are the limits of that visibility?
Companies need a clear, central view of how traffic moves across the business, which connectivity providers are involved, how the network is performing and whether individual sites are operating as expected. This requires a single source of truth across regions, sites and providers, bringing together information on services, performance, costs and where action is needed. This helps technology leaders identify bottlenecks, respond to outages, verify service performance and make better-informed decisions across markets and cloud environments. However, network visibility is only one part of the picture. It does not automatically reveal the sensitivity of the underlying data, how a SaaS provider processes it or every downstream dependency. The network provides valuable operational evidence, but it must work alongside application, cloud, identity and data-governance controls to give leaders a fuller view of where risks sit and whether the organization remains genuinely in control.
AI introduces dependencies on model providers, APIs, telemetry, vector databases and other services that may operate across jurisdictions. How should companies map those dependencies before putting sensitive workloads into production?
Businesses need to look beyond the AI model and understand the entire ecosystem supporting it. This simply means knowing where sensitive data enters, which models, APIs, databases and third parties interact with it, where those services operate, and what happens if one becomes unavailable. Clear ownership, permissions and fallback arrangements are equally important. This is becoming more urgent as agentic AI gains greater autonomy and access to enterprise systems. Singapore’s updated Model AI Governance Framework for Agentic AI reinforces the need to set clear boundaries, maintain meaningful human oversight, and continuously test and monitor agents.
For business leaders, the key question is whether the organization can explain the workload from end to end and demonstrate clear accountability for the key risks involved.
How can a company maintain sovereignty controls across multicloud and SaaS environments without creating a fragmented architecture that is difficult to operate or secure?
The most effective approach is not to build a separate technology stack for every market, as that can create unnecessary complexity and operational risk. Businesses should establish a common framework for governance and connectivity, then adapt individual workloads where local requirements justify it. Policies governing access, resilience and accountability should remain consistent, even when hosting, processing or routing arrangements differ. The principle is to standardize the controls rather than every component. This gives multinational businesses the flexibility to meet market-specific requirements while retaining the interoperability needed to operate effectively across APAC.
What trade-offs do companies encounter when they localize processing or data, particularly around latency, resilience, cost and access to advanced AI services?
Localization can give businesses greater control, help meet regulatory or customer requirements, and, in some cases, improve latency. However, the trade-offs can include fewer provider choices, higher costs and potentially limited access to advanced cloud or AI services. Replicating environments across markets can make governance more complicated, while excessive localization may reduce the ability to shift workloads when a provider, route or site experiences disruption. A single local path is not resilient simply because it is compliant; businesses should consider route, provider and technology diversity as part of the design. Business leaders should therefore assess localization workload by workload. The key question is whether local processing delivers a clear regulatory, operational or performance benefit, and whether that benefit justifies the potential impact on resilience, interoperability, cost and access to technology.
How should organizations classify workloads and data when deciding what should remain local, what can be processed regionally and what can safely use global cloud or AI services?
Organizations should classify workloads based on four considerations: data sensitivity, regulatory requirements, business criticality, and the consequences of losing access or control. Highly sensitive or regulated workloads may need to remain local, while others can operate regionally where the relevant jurisdictions, providers and data flows are understood. Lower-risk workloads may be suitable for global services, provided the right safeguards are in place. Importantly, this should not be treated as a one-time decision, as risks evolve when AI moves from pilot to production. Singapore’s 2026 guidance on personal data in generative AI reinforces this lifecycle approach by emphasizing clear responsibilities, appropriate safeguards and regular reviews, including for agentic AI systems.
What should technology teams require from network, cloud and AI providers in contracts or technical controls around routing, logging, jurisdiction, failover and access to customer data?
Technology teams should ask providers for evidence rather than rely on broad assurances. Contracts and technical documentation should clarify where services operate, how traffic is routed, what is logged, who can access customer data, and how outages or jurisdictional changes are handled. They should also identify downstream providers, service ownership, escalation paths and failover responsibilities. This is particularly important for multinational businesses, where accountability can become blurred across several providers. While specific terms will vary by workload and jurisdiction, organizations must ultimately be able to verify how services operate, respond when circumstances change and maintain control.
What evidence should executives and boards ask for to determine whether a digital-sovereignty strategy is actually working rather than becoming a compliance checkbox?
Boards should look for evidence that a sovereignty strategy works in practice, not just on paper. That includes whether sensitive workloads have clear ownership, whether access and data movement can be audited, whether resilience arrangements have been tested, and whether teams can respond effectively when conditions change. Commercial oversight is equally important. The IDC InfoBrief commissioned by Expereo found that 41 percent of APAC technology leaders are concerned about losing track of AI-related costs and ROI as adoption deepens. An effective strategy should therefore deliver measurable improvements in control, resilience and accountability while enabling the organization to scale and demonstrate business value.
Looking across APAC over the next 12 to 24 months, which regulatory, infrastructure or AI developments do you expect to have the greatest impact on how multinational companies design their regional technology environments?
Three forces are likely to shape regional technology environments over the next 12 to 24 months: increasingly complex data and AI governance, the deeper integration of AI into everyday operations, and continued differences in infrastructure readiness across APAC. Together, these are likely to move digital sovereignty beyond policy discussions and into architecture, procurement and risk management.
The ASEAN Digital Masterplan 2030 reflects this direction through its focus on seamless infrastructure, a resilient and trusted digital ecosystem, and AI-driven transformation. However, turning these ambitions into business outcomes will depend heavily on network readiness. The IDC InfoBrief commissioned by Expereo found that only 9 percent of APAC organizations consider their networks fully ready for new initiatives, while 57 percent need greater flexibility and scalability. Without resilient, scalable networks, AI, cloud and digital-sovereignty strategies will be much harder to operationalize across the region.
Eric Wong is President of Asia Pacific and Global Wholesale at Expereo.
Editor’s note: This Q&A has been lightly edited for clarity and TNGlobal house style. The substance of the interviewee’s responses has been preserved.
Share your perspective: TNGlobal welcomes contributed insights and expert commentary from across Asia’s technology and innovation ecosystem. Submit a contribution for editorial consideration, or explore more conversations in our TNGlobal INSIDER and TNGlobal Q&A and Interviews archive.