AI assistants that can read email, call APIs, move files or change system state raise a different access-control problem from chatbots that only generate content. Once an agent can act with credentials, the security discussion shifts toward identity, privilege, auditability and who owns the agent throughout its lifecycle.
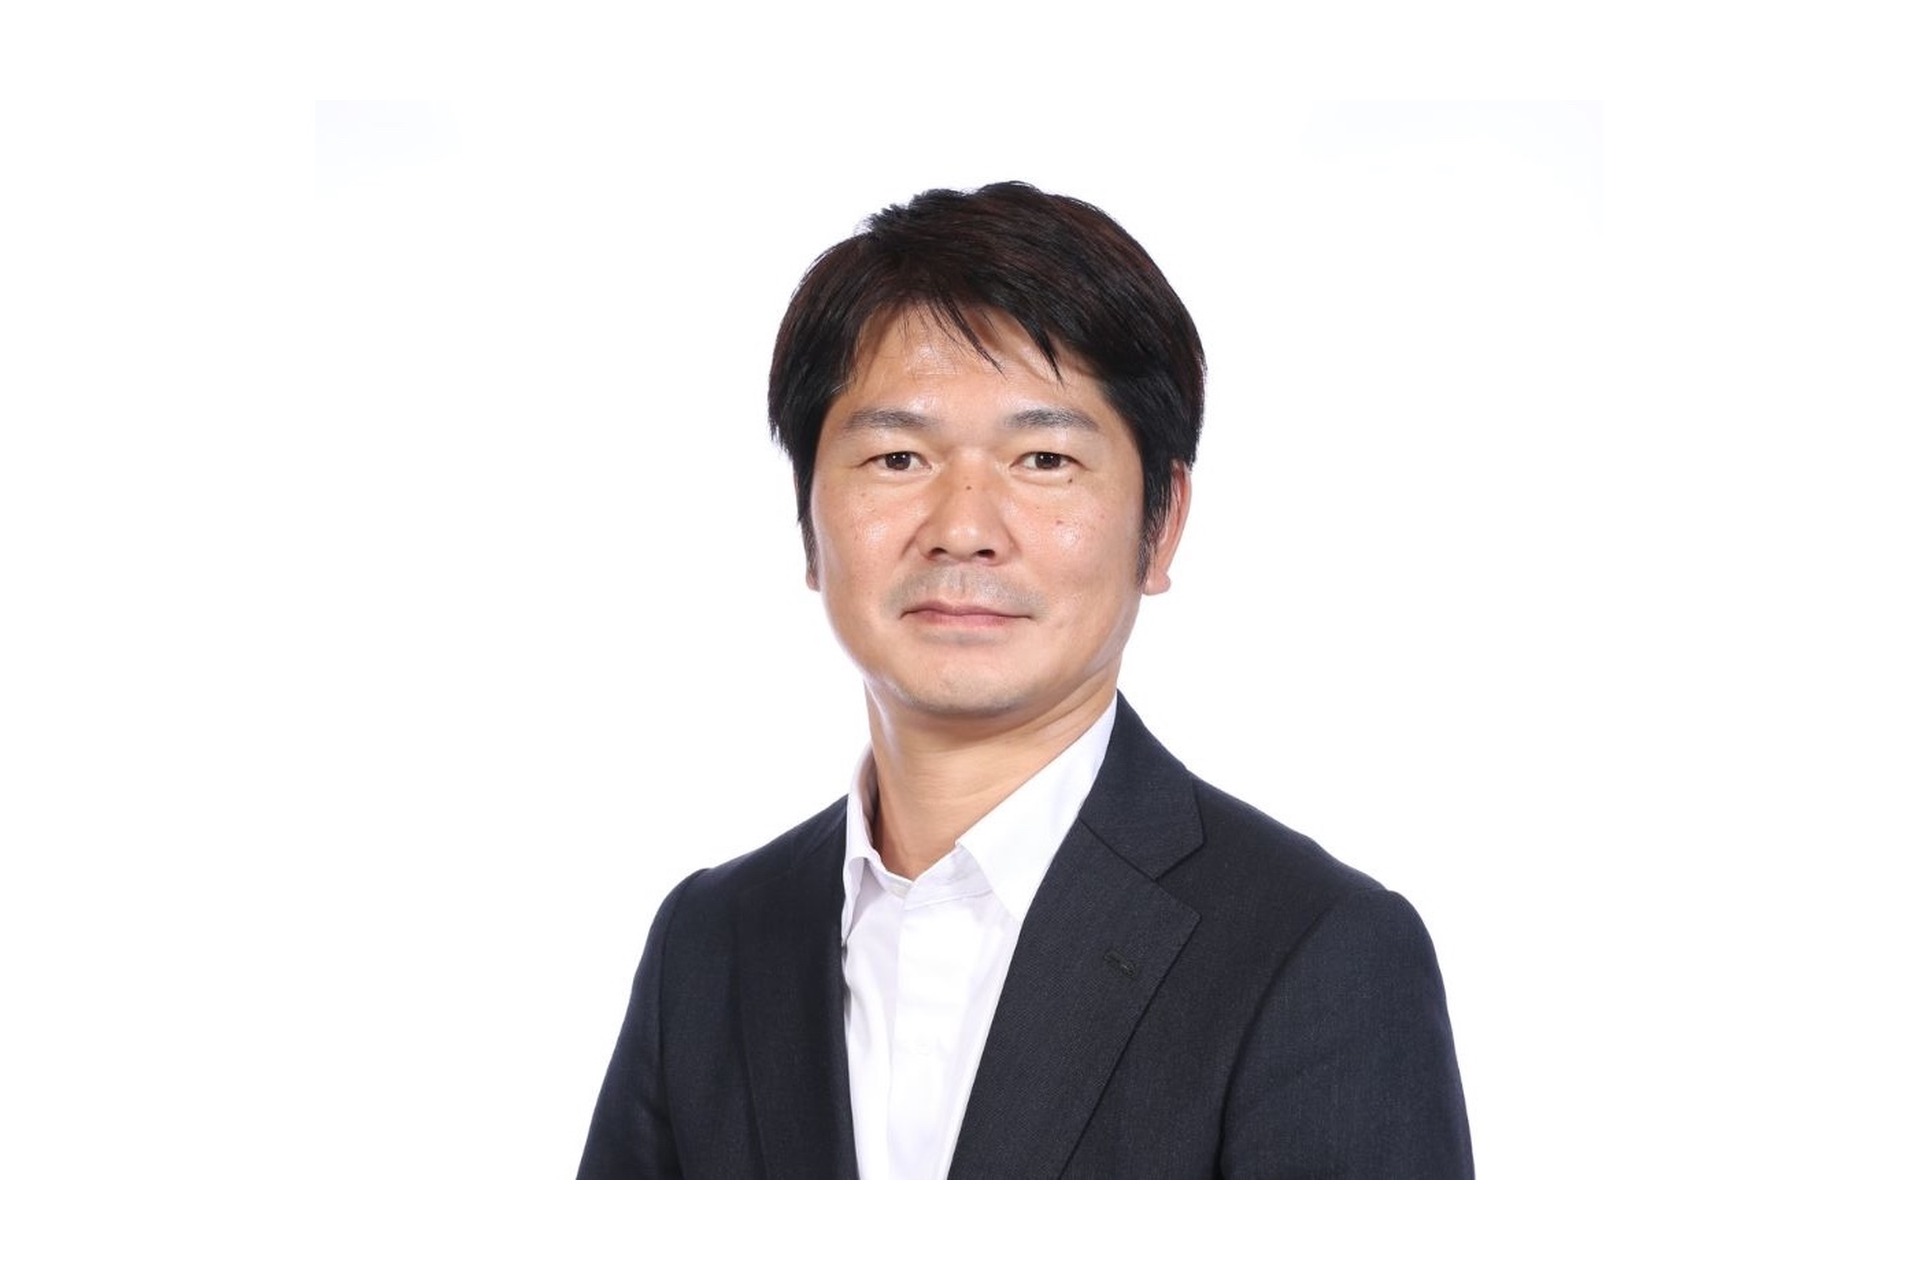
In this TNGlobal Q&A, Takanori Nishiyama, Senior Vice President of APAC Sales and Country Manager, Japan at Keeper Security, shares insights on when AI agents should be treated as privileged identities, how just-in-time access and credential management apply, where human approval should remain mandatory, and how governance is evolving across Asia Pacific.
Nishiyama has previously written for TNGlobal about privileged-access management. The research figures and security recommendations below reflect his responses and the cited sources.
As AI assistants and agents move from generating content to accessing inboxes, files, cloud services and enterprise applications, at what point should organizations stop treating them as productivity tools and start treating them as privileged identities?
An AI agent becomes a privileged identity the moment it can authenticate to a system and act on data without human approval at each step. Every agent introduces a new identity, a new attack surface and a new compliance obligation, and that threshold arrives earlier than most organizations expect. Gartner predicts that 40 percent of enterprise applications will include task-specific AI agents by the end of 2026, up from less than 5 percent in 2025.
Once an agent reads an inbox, moves a file or calls an API, it carries the same access as a privileged user and must be subject to the same identity governance. Research from Keeper Security finds that 89 percent of senior IT leaders struggle to manage their growing identity footprint as AI adoption accelerates. Organizations must treat every agent as a distinct, verifiable identity from the day it is deployed. Assign an owner, define its permissions and bring it under privileged-access controls.
Many enterprises already have controls for employees, service accounts and administrators. What is materially different about governing AI agents, and where do traditional identity and privileged access models fall short?
AI agents operate at a fundamentally different cadence. They spin up on demand, are often created by developers or other applications, and they frequently act using credentials delegated from a human. That combination breaks the assumption that every action maps to a person.
A Keeper Security survey of 109 cybersecurity professionals at RSA Conference 2026 found that 46 percent of respondents give AI-powered tools access to critical systems and data, while 76 percent do not govern those identities consistently under privileged-access policies. Privileged Access Management (PAM) already solves this class of problem for human identities. Organizations should extend the same PAM discipline to every agent and machine account rather than leaving them outside the security perimeter.
Standing privileges are often convenient for automated workflows, but they also increase the impact of a compromised or manipulated agent. How practical is just-in-time or least-privilege access for AI agents without breaking the workflows businesses are trying to automate?
Just-in-time (JIT) and least-privilege access should be table stakes for AI agents. Every security team should strive for zero standing privilege, which means no user holds permanent credentials and instead receives time-limited, policy-enforced access only when needed.
Standing privileges sitting idle are the credentials cybercriminals target because nobody owns them or checks on them and, therefore, they can persist indefinitely. Security teams should scope each agent to a single task, grant access for the duration of that task and revoke it automatically when the task ends. Workflows need reliable access at the right moment, which JIT provisioning delivers without leaving a standing target behind. A modern PAM solution can deliver JIT access and endpoint privilege management for AI agents through integrations that use the same workflows developers already have in their toolkit.
AI agents may use API keys, service accounts, OAuth tokens or delegated user permissions across multiple systems. What should organizations do to prevent credential and secrets sprawl as agent deployments scale?
Credential and secrets sprawl grows fastest when agents scale, and the fix is to remove long-lived secrets from the places agents touch. GitGuardian’s State of Secrets Sprawl 2026 report found 28.65 million new hardcoded secrets in public GitHub commits during 2025, a 34 percent year-over-year increase, and identified 24,008 unique secrets exposed in Model Context Protocol (MCP) configuration files, a new leak surface tied directly to agent tooling.
Every API key, token and service-account credential should be stored securely in a centralized vault rather than in code, configuration files or chat tools. They should be automatically rotated, and each agent should be given a distinct identity so security teams can trace and revoke its access if necessary. MCP connections deserve particular care since they wire agents into live systems and data. Credentials should reach an agent at runtime and expire with the task, never live inside the agent indefinitely.
Prompt injection and malicious instructions can cause an otherwise legitimate AI agent to misuse access it was already granted. Which controls at the identity and access layer can reduce that risk, and which parts of the problem cannot be solved by identity security alone?
Prompt injection begins at the model layer, outside the identity-security perimeter. Identity controls cannot prevent it, but they can limit the damage by restricting what a compromised or manipulated agent can access or do. IBM’s 2026 Cost of a Data Breach analysis found that 92 percent of organizations that suffered an AI-related breach lacked proper AI access controls. Manipulation may start at the model, but the access layer decides how far it spreads.
Least-privilege access, zero standing privilege and JIT access shrink the blast radius, while real-time session monitoring surfaces misuse as it happens. What identity security cannot address is the model itself reading malicious instructions from a document, email or web page and treating that information as trusted input. Closing that gap requires input validation, content filtering and a human in the loop to review consequential actions.
Where should organizations draw the line between autonomous action and mandatory human approval? Are there specific types of actions, such as changing permissions, moving money, deleting data or exporting sensitive information, that should almost always require an additional checkpoint?
Organizations must require human approval before permitting any action that cannot be undone or that moves anything of value outside the organization. Changing permissions, moving money, deleting data and exporting sensitive information almost always qualify, regardless of how confident the agent appears.
This is the type of runtime control addressed by Singapore’s Safeguards for Agentic Finance at Runtime (SAFR), an industry-developed framework created under the Monetary Authority of Singapore’s BuildFin.ai initiative. It defines how agent actions are authorized, when human oversight activates and what the system records at consequential decisions.
Organizations can allow agents to act autonomously on low-risk, reversible tasks such as drafting, summarizing and routine retrieval. However, it is imperative to require human approval for actions that carry lasting financial, legal or data-loss consequences. Security teams should map each agent’s possible actions to risk tiers before deployment, ensuring the approval gate is in place before it is activated.
What telemetry should security teams capture to understand what an AI agent actually did, which identity or credential it used, what data it accessed and whether the action originated from a human request, an automated workflow or a potentially manipulated instruction?
Organizations should prioritize four essential pieces of telemetry: the agent’s verifiable identity, the credential or token it used, the systems and data it touched, and the origin of each request.
Session recording and audit logs make agent activity as reviewable as any privileged human session. However, speed matters as much as coverage. Keeper Security research found that 72 percent of organizations do not detect credential misuse in real time, with most taking hours and, in some cases, days or weeks to identify unauthorized privileged access. Organizations should feed agent telemetry into privileged-account monitoring and alert on anomalies. An agent reaching for data outside its defined task is the clearest red flag.
Across Asia Pacific, are you seeing meaningful differences in how organizations approach AI-agent identity and privileged access? Which sectors or markets appear to be moving fastest, and where are the largest governance gaps?
Asia Pacific shows real divergence in how organizations govern AI agents, driven primarily by each market’s regulatory posture. Financial services and government are moving fastest.
In Japan, the Financial Services Agency has published an AI Discussion Paper, while the Ministry of Economy, Trade and Industry and Ministry of Internal Affairs and Communications have issued AI Guidelines for Business. Singapore has moved further on agent-specific guidance, with the Infocomm Media Development Authority launching its Model AI Governance Framework for Agentic AI in January 2026. MAS has also worked with financial institutions and FinTechs on the SAFR industry framework for runtime controls in agentic finance.
Looking ahead over the next 12 to 24 months, what AI identity or access risk do you think enterprises are still underestimating, and what part of the current agent-security conversation may be receiving more attention than it deserves?
Enterprises underestimate the risk of unowned agents. When an agent is deployed, many organizations do not assign a single accountable owner for its lifecycle. Without that ownership, provisioning happens but rotation, monitoring and offboarding do not, and agents can persist long after they should be decommissioned, with their access lingering and credentials accumulating across systems.
The industry spends considerable energy on threat-detection frameworks and model safety, which matter, but the operational fundamentals are just as important. To secure agents, an owner should be assigned before they go live, the agent’s lifecycle should be defined, and it should be automatically deprovisioned when that period expires. Agents should be held to the same session-recording and auditing standards as human identities throughout. Organizations cannot detect threats against agents they do not have visibility into, and that visibility will not exist until someone is held accountable for them.
Takanori Nishiyama is Senior Vice President of APAC Sales and Country Manager, Japan at Keeper Security. Before joining Keeper, he spent about a decade at VMware in end-user computing roles across Japan and Asia Pacific and previously held roles at Red Hat and EMC.
Editor’s note: This Q&A has been lightly edited for clarity and TNGlobal house style. The substance of the interviewee’s responses has been preserved.
Share your perspective: TNGlobal welcomes contributed insights and expert commentary from across Asia’s technology and innovation ecosystem. Submit a contribution for editorial consideration, or explore more conversations in our TNGlobal INSIDER and TNGlobal Q&A and Interviews archive.
The critical role of SysAdmins in protecting privileged access